
Key takeaways
- CEO Jensen Huang resigned after his relationship with a Megaspeed executive became public; the Singapore data center company is under federal investigation for allegedly funneling Nvidia chips to China.
- Intelligence services exploit personal relationships lasting years rather than weeks, seeking policy insight and identifying obstacles to favorable regulations rather than stealing technology directly.
- Corporate security teams are chronically underfunded, narrowly scoped to facility and cyberattack defense, and lack clear authority over executive relationships that create intelligence vulnerabilities.
Two Leadership Departures, One Unfolding Scandal
In August, David Reber, Nvidia’s chief security officer, announced his departure, citing personal health concerns. Reber had served as CSO for four years and spent seven years at the company overall. In a LinkedIn post, he disclosed that he had been diagnosed with young-onset Parkinson’s disease more than two years earlier. “This wasn’t a pivot I had planned,” he wrote. “But I know what needs to come first: family and health.”
His replacement, Saša Zdjelar, came from a different background. She spent seventeen years at ExxonMobil in Houston, rising to senior IT manager, then spent one year at Salesforce before joining ReversingLabs, a cybersecurity company where she worked for several years before moving to Nvidia.
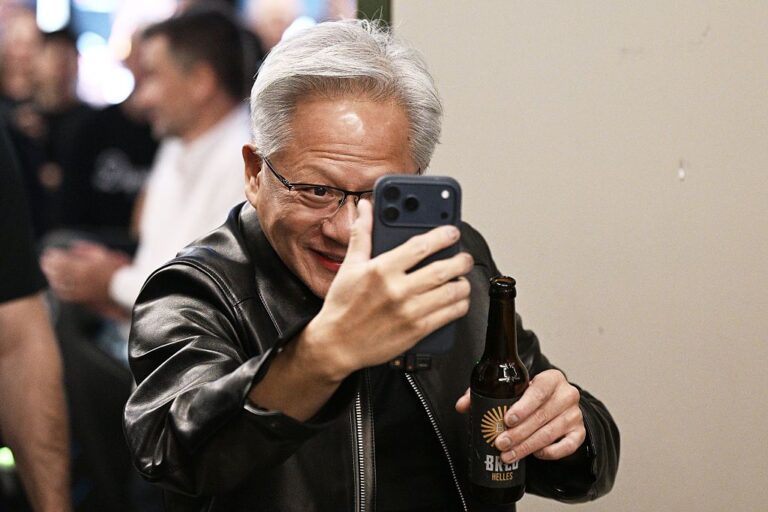
Two and a half months after Reber’s departure, CEO Jensen Huang announced his resignation. The circumstances behind it were public and substantial. Huang had been involved in a relationship with an executive at Megaspeed, a Singapore-based data center company that U.S. investigators suspect of diverting Nvidia chips to China without authorization. Megaspeed has denied any wrongdoing. Beyond that relationship, additional affairs with Nvidia employees came to light. According to The New York Times, five Nvidia employees confirmed Huang’s involvement with a vice president who reported directly to him. Reuters later reported a second relationship with a separate Nvidia employee.
The sequence raised an obvious question: what did Nvidia’s security organization know about these relationships, and when did it know? Neither Reber nor Zdjelar responded to inquiries about the transition or what the security team was aware of. Nvidia declined to provide comment.
What the Security Team Should Have Known
Different Information, Same Risk
Relationships between a CEO and employees typically fall under the purview of human resources, legal counsel, and the board. Security teams do not usually investigate romantic entanglements. Yet the circumstances in this case blur those lines. Huang’s involvement with someone at Megaspeed, a company under federal investigation, was not merely an internal workplace matter. It involved a person connected to a firm suspected of illegal activity and simultaneously presented a potential intelligence vulnerability.
Huang’s affairs with Nvidia employees, while different in character, presented another form of exposure. Security specialists say that any affair, whether internal or external, can provide leverage to a foreign intelligence service against an executive who wants the relationship concealed. The leverage becomes particularly acute when the other party has access to sensitive information or works at a company already under scrutiny.
Who Knew What
Within Nvidia, information about these matters was scattered across the organization. The company’s top lawyer was engaged with the government’s investigation into Megaspeed more than a year ago, according to The New York Times. Huang’s relationships with employees were not secret from his colleagues; five Nvidia employees spoke to the Times about his involvement with the vice president, and additional people knew of the second relationship. What remains unclear is whether any of that information reached the security function and, if it did, what action security was empowered to take.
How Foreign Intelligence Exploits Personal Vulnerability
Nicholas Eftimiades, a retired senior intelligence officer who has trained over one thousand corporate security professionals, offered insight into how adversaries weaponize personal relationships. Intelligence services, he explained, gather much of their information through ordinary conversation rather than hacking. That reliance on human intelligence makes it extraordinarily difficult for corporate security teams to detect emerging threats in real time.
The approach is not new, particularly where China is concerned. “Any executive dealing with the country will tell you that they’ve been approached,” Eftimiades said. Diplomatic history offers examples: U.S. diplomats have walked into hotel rooms to find women on beds in scenarios engineered to create compromise. What distinguishes current operations from the Cold War era is the longevity of the relationships intelligence services cultivate. Modern operations often sustain relationships over years rather than weeks, making them harder to recognize as hostile activity.
What a rival intelligence service typically wants is not technology itself but policy information and insight. Eftimiades offered a hypothetical: if a CEO mentions that a particular policy change cannot move forward because the board opposes it, that statement reveals who the obstacle is. An intelligence service then asks, “Who’s the sticking point here?” and works to gain access to that person’s communications. The goal is understanding who in government or industry is most likely to resist changes to export rules or regulations that might favor the intelligence service’s interests.
The Resource and Scope Problem in Corporate Security
Underfunding as a Structural Issue
Security teams operate under consistent budget pressure. Unlike business units that generate revenue, security is categorized as a cost center. As a result, leadership frequently resists security recommendations by capping spending at compliance minimums. Eftimiades said it is “astonishingly common” for CEOs to tell security teams: “not a nickel more than compliance.”
Beyond funding, many organizations define security too narrowly. Don Aviv, CEO of the corporate investigations firm Interfor International, and Jeremy Hurewitz collaborated on an opinion piece in The Hill arguing that companies “still approach security primarily as a matter of protecting facilities, preventing cyberattacks, and responding to physical threats.” They advocated for a broader remit: “security teams need to pay greater attention to insider threats, including the cultivation of executives and employees by foreign intelligence services, suspicious business relationships, conflicts of interest and attempts to obtain sensitive information through trusted personal contacts.”
Limits That Even Well-Resourced Teams Face
Even an expansively defined, well-funded security organization has structural boundaries. Some intelligence risks lie entirely outside what any team can control. Eftimiades sketched a scenario in which a CEO says something revealing to a board member or peer, and that information then reaches an intelligence service. The adversary now knows who is blocking their goals and redirects resources toward compromising that person. “Intel world tends to be like cancer,” Eftimiades said. “Once it gets into the body, it looks to spread and looks to reach out.”
The Technology That Augments Intelligence Operations
Foreign intelligence agencies combine human intelligence with digital tools. Eftimiades cited IMSI catchers, which are devices that mimic cell towers and force nearby phones to connect through them, as one example. A basic model costs approximately one thousand dollars and fits in a suitcase, though government-grade versions cost far more. Cases involving Chinese espionage surfaced last year where these devices played a role. Huang’s phone was presumably hardened to detect or prevent such intrusions, though Eftimiades cautioned that it remains unknown whether such devices were deployed against him.
What Nvidia’s Board and Federal Investigators Must Determine
The question of what Nvidia’s security team knew and when it knew it will be clarified through two processes: the company’s independent board investigation and ongoing federal inquiries. Eftimiades expressed hope that the scandal serves as “a wake-up call” for U.S. industry broadly, which he characterized as “clueless” about China’s intelligence tactics. He estimated that China has succeeded in acquiring trillions of dollars in American intellectual property. “Whatever we think we’re doing isn’t working,” he said.
For Nvidia, the timing of Reber’s August departure and the subsequent revelations left the company’s security function defending questions it may not have been equipped to address. Reber’s health challenges were genuine and publicly disclosed. Zdjelar brings substantial experience. But the sequence of events created an optics problem that no organizational chart can fully resolve.
Source: TechCrunch
Frequently Asked Questions
When did David Reber leave Nvidia and why?
David Reber, who served as Nvidia's chief security officer for four years, departed in August citing a diagnosis of young-onset Parkinson's disease that he had received more than two years earlier.
What was Jensen Huang's relationship with Megaspeed?
Huang was in a relationship with an executive at Megaspeed, a Singapore-based data center company that U.S. investigators suspect of diverting Nvidia chips to China without authorization. Megaspeed has denied all allegations.
Why is it difficult for corporate security teams to detect intelligence threats?
Foreign intelligence services gather much of their information through ordinary conversation rather than hacking, which makes it extremely difficult for security teams to identify emerging risks in real time. Intelligence agencies also cultivate relationships over years rather than weeks, making them harder to recognize.
